Industries
Why software employees leave and how to understand why
Engineers and product staff leave for many reasons beyond salary. How to run an exit conversation in a software company, read the pattern and act on it.
6 min readRead articleA cybersecurity firm sells expertise and trust, and both walk out when people do. Here is how to run the people side around sensitive work.
Not sure what you need? Tell us about your business in six short steps and we will come to the first meeting prepared.
Share your requirementsA cybersecurity firm helps other businesses find weaknesses, monitor threats and respond to incidents. Its people include penetration testers, security analysts, consultants working on audits and policy, and teams who watch customers' systems in a security operations centre around the clock. The firm handles customers' most sensitive information, so confidentiality and conduct matter more than in most businesses. Skills are scarce, learning never stops, and a good tester or analyst is approached by competitors often. Incident work arrives without notice, and a bad night can follow a quiet week. See also HR for IT and software.
Who does the work
Shift work in the operations centre
Monitoring runs through nights and weekends, and analysts tire of repetitive alerts, so the same seats keep turning over.
Burnout after incidents
Responders work long hours during an attack, and there is rarely a rule for rest, recognition or a quiet period afterwards.
Confidentiality depends on conduct
Staff see customer data and weaknesses, and without clear rules and reminders the firm relies on trust alone.
Testers are poached
Experienced testers and responders receive offers often, and projects are tied to named individuals the customer has met.
Learning time gets squeezed
Skills date quickly, but billable work leaves no hours for research, labs or study, so people feel they are falling behind.
Consultants and technical staff are measured differently
Billing targets suit consultants but frustrate researchers, and one appraisal scheme satisfies neither.
Career paths are unclear
A strong analyst does not know whether growth means a deeper technical role, a lead role or a move to consulting.
Write a plain confidentiality and conduct policy
What staff may do with customer data and access, what must be reported and what happens on a breach, signed and explained at joining. HR policies and governance covers drafting; have the final wording reviewed by a qualified professional.
Design the SOC rota to reduce fatigue
Fixed rotation patterns, limits on consecutive night shifts and a path out of monitoring into response or research. The attendance and shift process records it.
Set a post-incident routine
Rest or time in lieu after long response work, a short debrief and recognition, agreed before the next incident rather than negotiated during it.
Protect time for learning
A fixed number of hours each month for research and certification study, planned into utilisation. The learning and development process shows how to track it.
Offer two career tracks
A technical track and a consulting or management track with separate measures, so appraisal fits the work. See performance management.
Confirm with a qualified professional. What applies to you depends on your business, your state and your arrangements, and it changes. This page describes practice. It does not state a legal position.
Clear, written rules on confidentiality, device and access use, and conduct that staff can follow.
A fair SOC rota with limits on night work and a record that supports payroll and rest.
Protected learning hours and a plan for the certifications and skills the firm needs.
Appraisal measures that suit analysts, testers and consultants differently.
Every engagement starts by recording where you stand, and every later report compares against that. We do not promise outcomes. Start with a free conversation, or see the paid HR Diagnostic.
From the GullyHR blog: one on HR in information technology and software, and one on each of the topics this page points to.
Engineers and product staff leave for many reasons beyond salary. How to run an exit conversation in a software company, read the pattern and act on it.
6 min readRead article
A practical contents list for an employee handbook in a growing Indian business: what to cover, what to leave to policies, and how to keep it usable and current.
5 min readRead article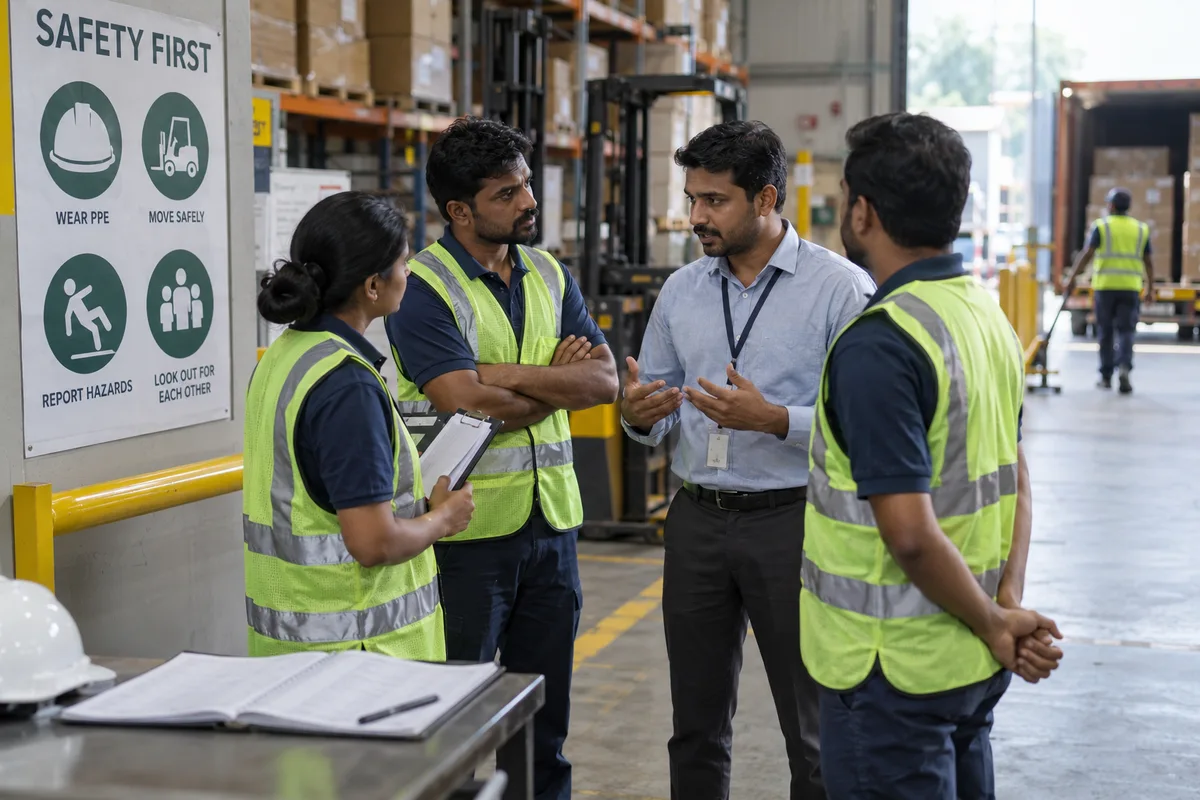
A laminated notice, an annual drill, and an incident register with three entries in two years. What workplace health and safety looks like when it is real.
7 min readRead article
How to spot an unmanageable workload before it becomes an exit or an error, what to look at, how to talk about it and what to change, without guessing.
5 min readRead articleMore on the GullyHR blog.
Limit consecutive night shifts, rotate people through different types of work and show a path from monitoring to response or research. Repetitive alerts on fixed seats are the usual reason people leave.
How customer data and access may be used, what to do on a suspected breach, rules on devices and storage, and what happens after leaving. Have a qualified professional review the wording.
Agree in advance how extra hours are recorded and compensated, and give rest afterwards. Deciding it during an attack leads to disputes and resentment.
No. Consultants are naturally measured on delivery and billing, while researchers and testers need measures of depth, findings and contribution. Separate tracks keep both fair.
Offer interesting work, learning time, a visible path and market-aware pay. Review it each year rather than when an offer arrives.
We would go through confidentiality terms and whether everyone has actually signed and understood them, the run of night shifts in your operations centre, and what rest followed your last major incident. A practical first piece of work is a plain confidentiality and conduct policy, plus a rota that limits fatigue. Scope is agreed in writing after we talk.
All 5 business types in information technology and software · Find another business type
See all HR topics for information technology and software, or another industry.
Identify payroll leaks, record gaps and hiring bottlenecks in a free first conversation, and leave knowing what to fix first.
Know what you need? Share your requirements in four short steps.
Want the full picture? See the paid HR Diagnostic.
Prefer a quick message? Chat on WhatsApp