HR Audit for Growing Businesses in Cybersecurity companies
What this looks like in your business
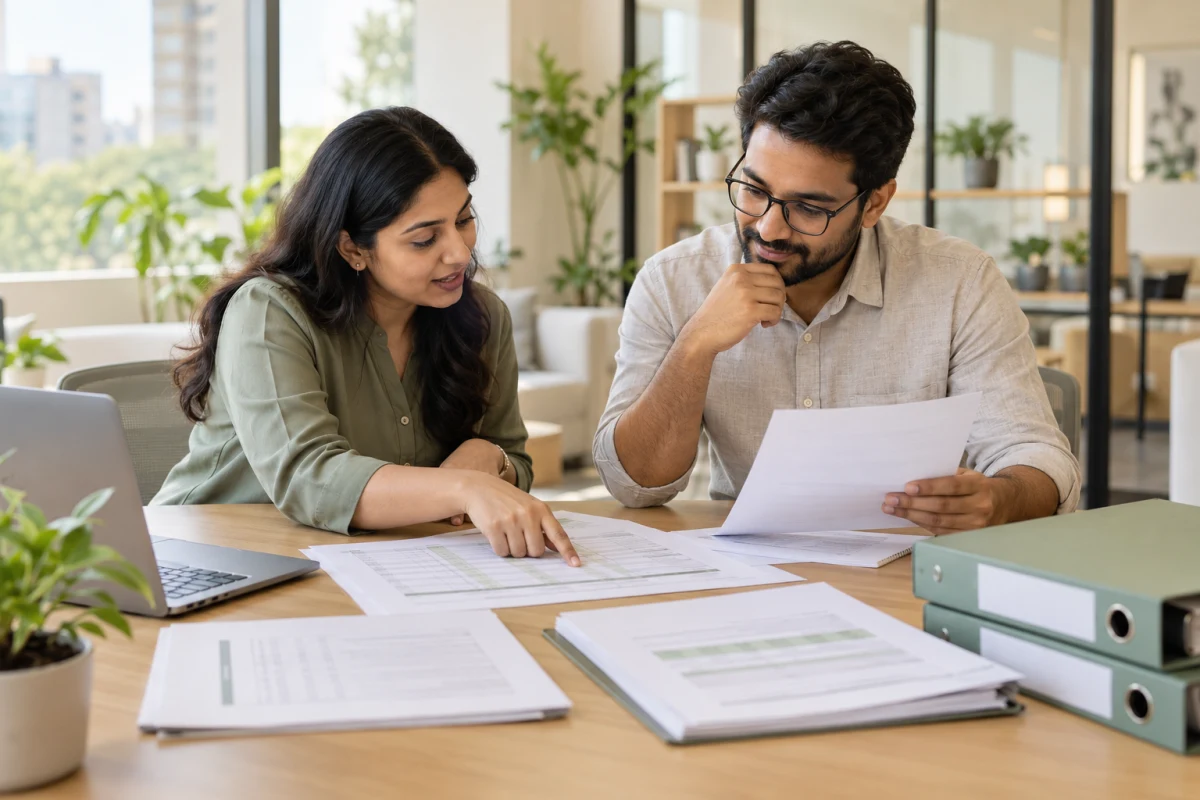
A security firm that has outgrown its founding team finds its HR running on memory and goodwill. The monitoring rota lives in a chat group, confidentiality undertakings sit in no agreed folder, and nobody can say how much time testers give to learning last month. An HR audit gives the owner a paid, written account of how HR really runs, drawn from signed letters, rota sheets, exit notes and the people who do the work. Owners reach for it when a tester resigns for a rival, an analyst is worn out after a long incident, or a client asks how staff are bound to secrecy.
Where HR strains in a security firm
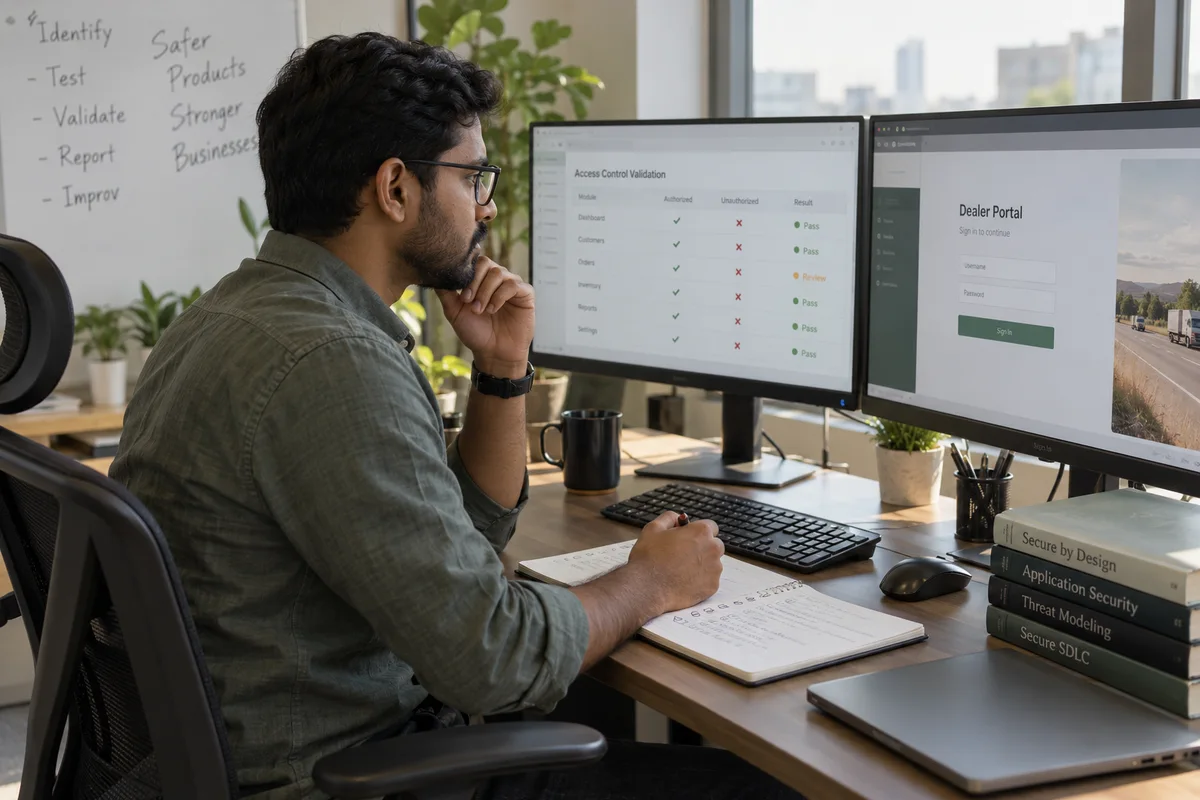
Security work does not keep office hours, and that is where the strain begins. A monitoring floor runs through nights and weekends, so the rota is the most important HR document in the building, yet in a smaller firm it is a spreadsheet owned by one team lead. Incident responders are pulled in at any hour, and the rest that should follow a long engagement is agreed by a handshake, if at all. Penetration testers are courted by rivals every week, and the firm learns of the offer only when the resignation arrives. Confidentiality is the other pressure point. Clients hand over networks, credentials and findings, so the firm's reputation rests on how each person behaves, not on any tool. If the signed terms are missing, out of date or never explained, the firm cannot show a client that its people are bound. An audit exists because these gaps are invisible from inside. Everyone is busy, the work gets delivered, and the weak joints in the people side show only after someone leaves or a client asks a hard question.
What the audit reads in your own records
GullyHR starts with the documents your firm already holds and the routines your leads already follow. For confidentiality, that means reading the signed terms for each person, checking dates against joining dates, and asking a few staff in plain words what they believe they are bound to do. For the monitoring floor, it means the last two months of rota sheets, counting consecutive night shifts per analyst and noting who covers sickness. For incident work, it means finding what rest or time off followed the last major engagement and who approved it. For testers and researchers, it means comparing how each is measured, because billable utilisation suits a consultant but misleads when applied to someone who researches. GullyHR also reads offer letters, role titles, pay bands and exit notes together, to see whether the numbers hang together and why people left. Each gap is written as a specific missing step, for example no signed terms for two joiners, or no rest rule after incidents, never as a general complaint about culture.
A worked audit across three groups
Take a managed security firm with a monitoring floor, a small testing team and a governance consulting group. Suppose the owner asks GullyHR to trace one joiner, one pay change and one exit in each group. For the analyst joiner, the audit finds the confidentiality terms were signed three weeks after the first shift, and the rota shows she worked four nights in a row in her first week. For the tester pay change, the approval sits in an email thread with no record of who agreed it, and the band does not match the one given to a colleague hired earlier. For the consultant who left, the exit note records no handover of client documents and no reminder of ongoing confidentiality duties. Each finding is rated, and the plan sequences the fixes: signed terms before first shift, a written pay approval step, an exit checklist that names who collects client material. The owner decides which to do first. GullyHR does not change anything without that decision. Nothing is judged until the evidence is on the table.
Who owns what after the audit
An audit report is only useful if each finding has a named owner and a record that proves it is fixed. GullyHR settles this with the owner before the plan is final. Rota rules belong to the head of monitoring, who signs off any change to night cover. Rest after incidents is set by the incident lead and recorded by whoever keeps attendance, so time off is visible and not remembered. Confidentiality terms belong to the owner or the director who signs for the firm, with one person holding the signed set and checking it at every joining and exit. Learning time is agreed with delivery managers and written into how utilisation is read for each role family. What stays with the owner is every decision that touches pay, promotion, discipline and who is let go. GullyHR reports what it found and in what order to fix it. The owner's own legal adviser confirms any point where local rules apply, and the owner chooses which findings to act on this quarter.